If your security team has three people, a dozen tools, and a growing list of alerts, you already know the problem. You have more data than you can process and not enough context to know what matters. Exposure management gives small teams a structured way to find the risks hiding between disconnected systems and fix the ones that could actually hurt the business.
This article covers what exposure management is, why it matters when your team is stretched thin, and how it helps you move from reactive alert-chasing to focused, risk-informed action.
Key Takeaways: How Exposure Management Helps Small Security Teams
- Exposure management goes beyond vulnerability scanning by adding business context, identity risk, and misconfiguration data to your risk picture.
- Small teams benefit most because the approach replaces manual triage with AI-driven risk prioritization ranked by real-world impact.
- Hidden risks like orphaned accounts, misconfigured firewalls, and shadow IT often create the most dangerous gaps in your environment.
- Guardare unifies data from your existing security tools into one dashboard so your team can act on what matters first.
- Continuous exposure management reduces breach likelihood by turning one-time assessments into an ongoing, repeatable process.
What Is Exposure Management in Cybersecurity?
Exposure management is a cybersecurity approach that identifies, monitors, and prioritizes risks across your entire attack surface. It looks at more than known software vulnerabilities. It accounts for misconfigurations, identity risks, access control gaps, and the business context around each one.
Traditional vulnerability management focuses on finding CVEs and assigning severity scores. Exposure management adds layers of context: Is the vulnerable asset internet-facing? Does it store sensitive data? Is the user associated with it a privileged account? That context determines whether a finding is urgent or can wait.
Gartner formalized this thinking with its Continuous Threat Exposure Management (CTEM) framework, a five-stage cycle of scoping, discovery, prioritization, validation, and mobilization. The framework treats exposure reduction as a continuous discipline rather than a periodic audit.
Why Small Security Teams Face Outsized Exposure Risk
A company with 80 employees faces many of the same attackers as a company with 8,000. The difference is staffing. Small and mid-sized businesses typically rely on one or two IT professionals who manage security alongside networking, help desk, and infrastructure. Dedicated security risk assessments often happen once a year, if at all.
According to the Verizon 2025 DBIR SMB Snapshot, system intrusion accounted for 53% of SMB breaches in the most recent reporting period. That figure reflects what happens when threat actors meet under-resourced defenses: they get in through gaps that a larger team would have caught.
Tool sprawl compounds the problem. Many organizations accumulate endpoint detection, identity management, cloud security, and compliance platforms that never share data with each other. Each tool generates its own alerts, creating noise that buries the signals that actually matter.
How Hidden Security Risks Slip Through Traditional Scanning
Vulnerability scanners are good at finding known CVEs in software packages. They are less effective at identifying the contextual risks that attackers increasingly exploit.
These hidden gaps often include orphaned user accounts that still have privileged access, misconfigured firewalls that expose internal services to the internet, and shadow IT applications that were never put through a formal security review.
A scan might flag 2,000 findings. Without business context, your team treats all of them with roughly equal urgency. That leads to patch fatigue, where the sheer volume of work causes the genuinely critical items to get lost in the backlog.
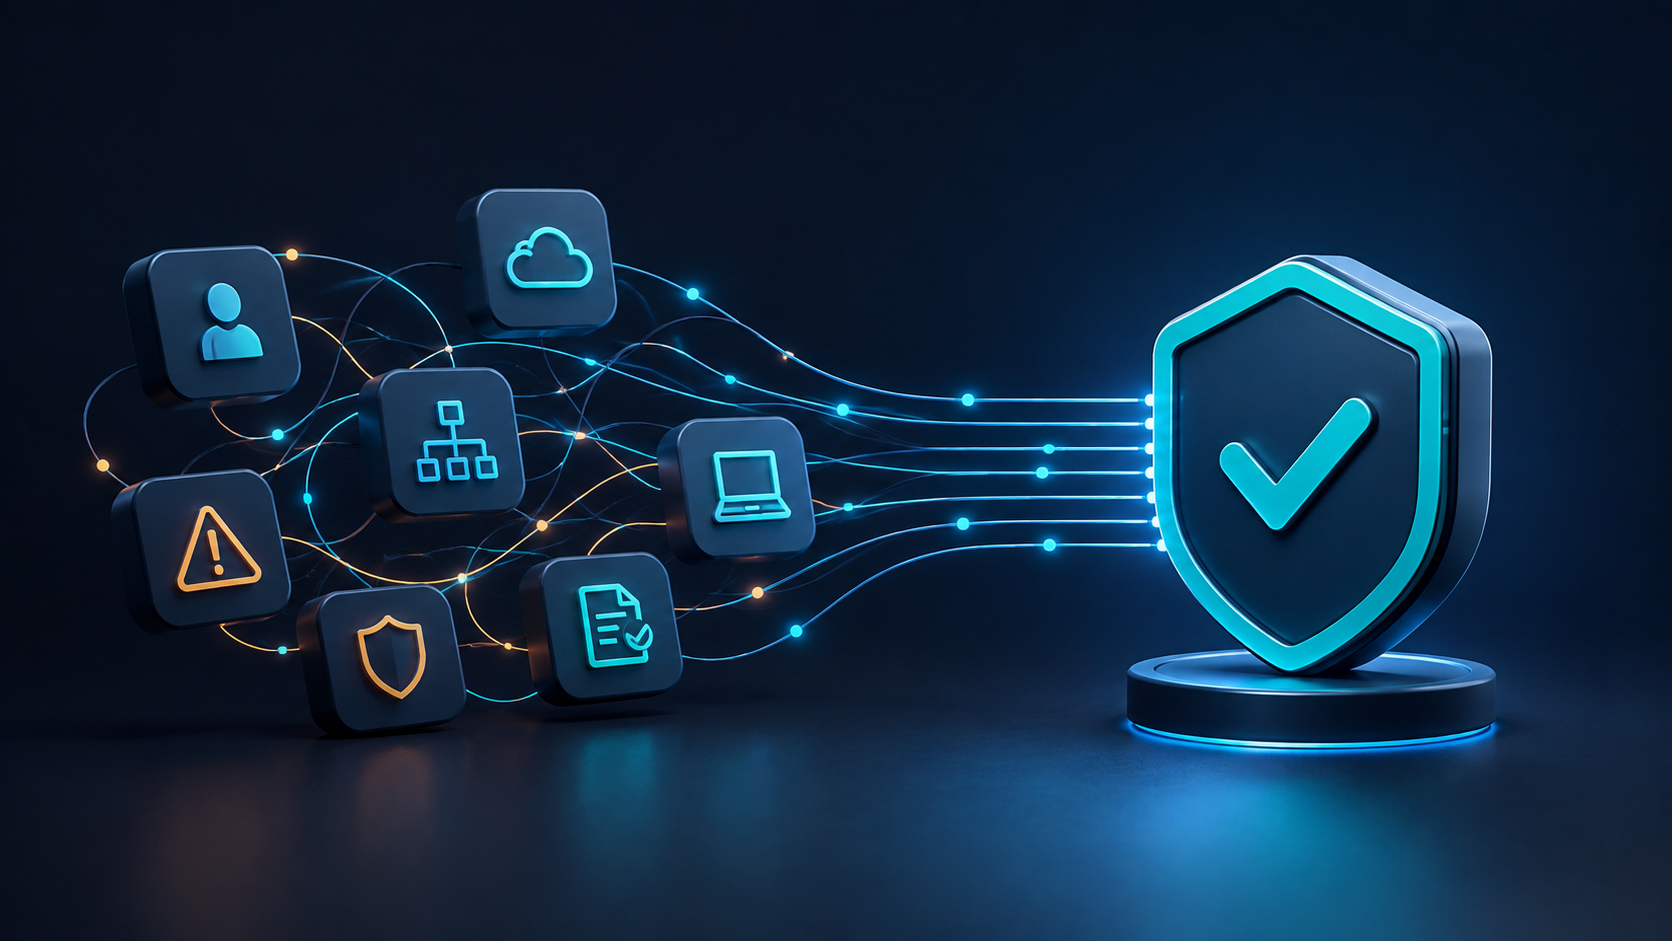
Exposure management closes that gap by correlating data across tools. It connects a vulnerable endpoint to the identity using it, the network segment it sits on, and the data it accesses. That correlation surfaces the 12 findings that represent real, exploitable risk rather than the 2,000 that represent theoretical possibility.
How Exposure Management Prioritizes Risk by Business Impact
Risk prioritization is where exposure management platforms deliver the most value for small teams. Instead of ranking findings by CVSS score alone, these platforms weigh factors like exploitability, asset criticality, user privilege level, and whether the affected system is internet-facing.
Guardare approaches this by building a unified risk graph of every user, device, and application in your environment. Its AI engine ingests signals from connected integrations, applies proprietary algorithms that factor in severity, exploitability, and business impact, and surfaces a prioritized list of actions ranked by what will reduce the most risk.
For a three-person IT team, that distinction matters. Knowing that a specific cloud admin account without MFA represents more immediate danger than an unpatched PDF reader on an air-gapped workstation means your limited hours go toward the work that actually protects the business.
What Does a Continuous Exposure Management Process Look Like?
Gartner's CTEM framework outlines five stages that form a repeating cycle. Small teams can adapt each stage to fit their capacity without losing the benefits of a structured approach.
Scoping defines what your organization cannot afford to lose. For an SMB, that list often includes your customer database, financial systems, and any cloud infrastructure hosting production applications. Discovery maps every asset, user, and connection point across your environment, including the shadow IT and forgotten test servers that traditional inventories miss.
Prioritization ranks exposures by business impact, not just technical severity. Validation confirms that a flagged exposure is actually exploitable in your specific environment. Mobilization turns findings into clear remediation steps with owners and deadlines.
Running this cycle continuously, rather than once a year, means your security posture visibility improves over time as gaps close and new risks are caught early.
How Guardare Helps Small Teams Manage Exposure Effectively
Guardare's Unified Cybersecurity Platform is built for teams that need clarity without complexity. It connects to the tools you already use, including endpoint detection, firewalls, identity providers, and cloud infrastructure, and unifies their data into a single dashboard.
The platform's AI Risk Management engine correlates risks across cloud, identity, endpoint, and community systems. It flags critical exposures, ranks them by potential impact, and delivers step-by-step remediation guidance in plain language. That means your IT manager does not need to be a deep security specialist to understand what to fix and why.
Guardare also addresses tool sprawl directly. Rather than replacing your existing stack, it learns from and connects everything you already have. The result is a single source of truth that turns fragmented data into actionable insight, helping your team focus on the few things that genuinely reduce risk.
Exposure Management vs. Vulnerability Management: Key Differences
Vulnerability management focuses on identifying known software flaws and assigning severity scores. It answers the question, "What is vulnerable?" Exposure management expands that question to, "What is vulnerable, reachable, and worth fixing first?"
The practical difference shows up in how your team spends its time. A vulnerability scanner might report a critical CVE on a server. An exposure management platform adds the context: that server is behind two layers of network segmentation, the CVE has no known exploit in the wild, and the only user with access is a read-only service account. Suddenly, that "critical" finding drops in priority.
For small teams with limited bandwidth, that contextual risk prioritization is the difference between burning hours on low-impact patches and spending time on the exposures that attackers would actually target.
Building a Realistic Exposure Management Roadmap for Lean Teams
You do not need a dedicated security operations center to start. Begin with an honest inventory of your assets: cloud accounts, user identities, endpoints, SaaS applications, and network infrastructure. Identify which of those assets store or process sensitive data.
Next, consolidate your security data. If your compliance reports, endpoint alerts, and identity logs live in separate consoles, you are making decisions with incomplete information. A platform that aggregates those signals into one view gives you the visibility to prioritize accurately.
Set a cadence for review. Monthly exposure reviews are a realistic starting point for a team of two or three. As your process matures, move toward continuous monitoring where the platform flags changes in real time and your team validates and remediates on a weekly sprint cycle.
In Conclusion: Exposure Management Turns Limited Resources Into Focused Protection
Small security teams will always face resource constraints. Exposure management does not eliminate that reality. What it does is make sure the hours you have go toward the risks that carry the most business impact.
By unifying data from your existing tools, adding business context, and prioritizing by exploitability and impact, exposure management replaces guesswork with a clear, repeatable process. Guardare's Unified Cybersecurity Platform gives your team that process in a single dashboard, so you can stop chasing alerts and start fixing the risks that matter.
FAQs About Exposure Management for Small Security Teams
What is exposure management in simple terms?
Exposure management is the process of finding, prioritizing, and fixing security risks across your entire environment. It goes beyond scanning for known vulnerabilities by adding business context, identity data, and configuration analysis to determine which risks need attention first.
How does exposure management differ from vulnerability management?
Vulnerability management identifies known software flaws. Exposure management expands the scope to include misconfigurations, identity risks, and access control gaps. It also ranks findings by real-world exploitability and business impact rather than relying on severity scores alone.
Why is exposure management important for small teams?
Small teams cannot address every alert. Exposure management surfaces the risks that carry the most potential damage and provides clear steps to remediate them. Guardare delivers this through AI-driven risk prioritization that helps your team act on what matters instead of drowning in noise.
Can exposure management work with tools I already have?
Yes. Exposure management platforms aggregate data from your existing security stack. Guardare connects to endpoint detection, firewalls, identity providers, and cloud infrastructure you already run, unifying their signals into a single prioritized view without requiring you to replace anything.
What hidden risks does exposure management uncover?
Common hidden risks include orphaned privileged accounts, misconfigured cloud storage, shadow IT applications, and gaps between overlapping security tools. Guardare's AI engine correlates data across these areas to flag exposures that individual tools miss on their own.